Security × Intelligence

Security you can see.
Intelligence you can use.

SI Studio builds tools where security meets AI: kernel-level eBPF observability for AI agents, reverse engineering for IoT firmware, and AI tools that help researchers read papers, understand code, and find sources faster.

7Products
3Focus areas
Local-firstYour data stays on your machine
agent-activity · demoLIVE
hook ⇄ eBPF cross-check0 events
// PRODUCTS

Three focus areas, seven products

From the OS kernel to the network gateway, from firmware binaries to academic papers: understand what is actually happening in the age of AI.

AI Agent Security 02

See exactly what AI coding assistants read, connect to, and execute on your machine.

Network & IoT Security 02

From home gateway traffic to device firmware, surface the risks hidden inside your devices.

AI Research Tools 03

Read papers, analyze code, and search sources, with AI saving researchers time.

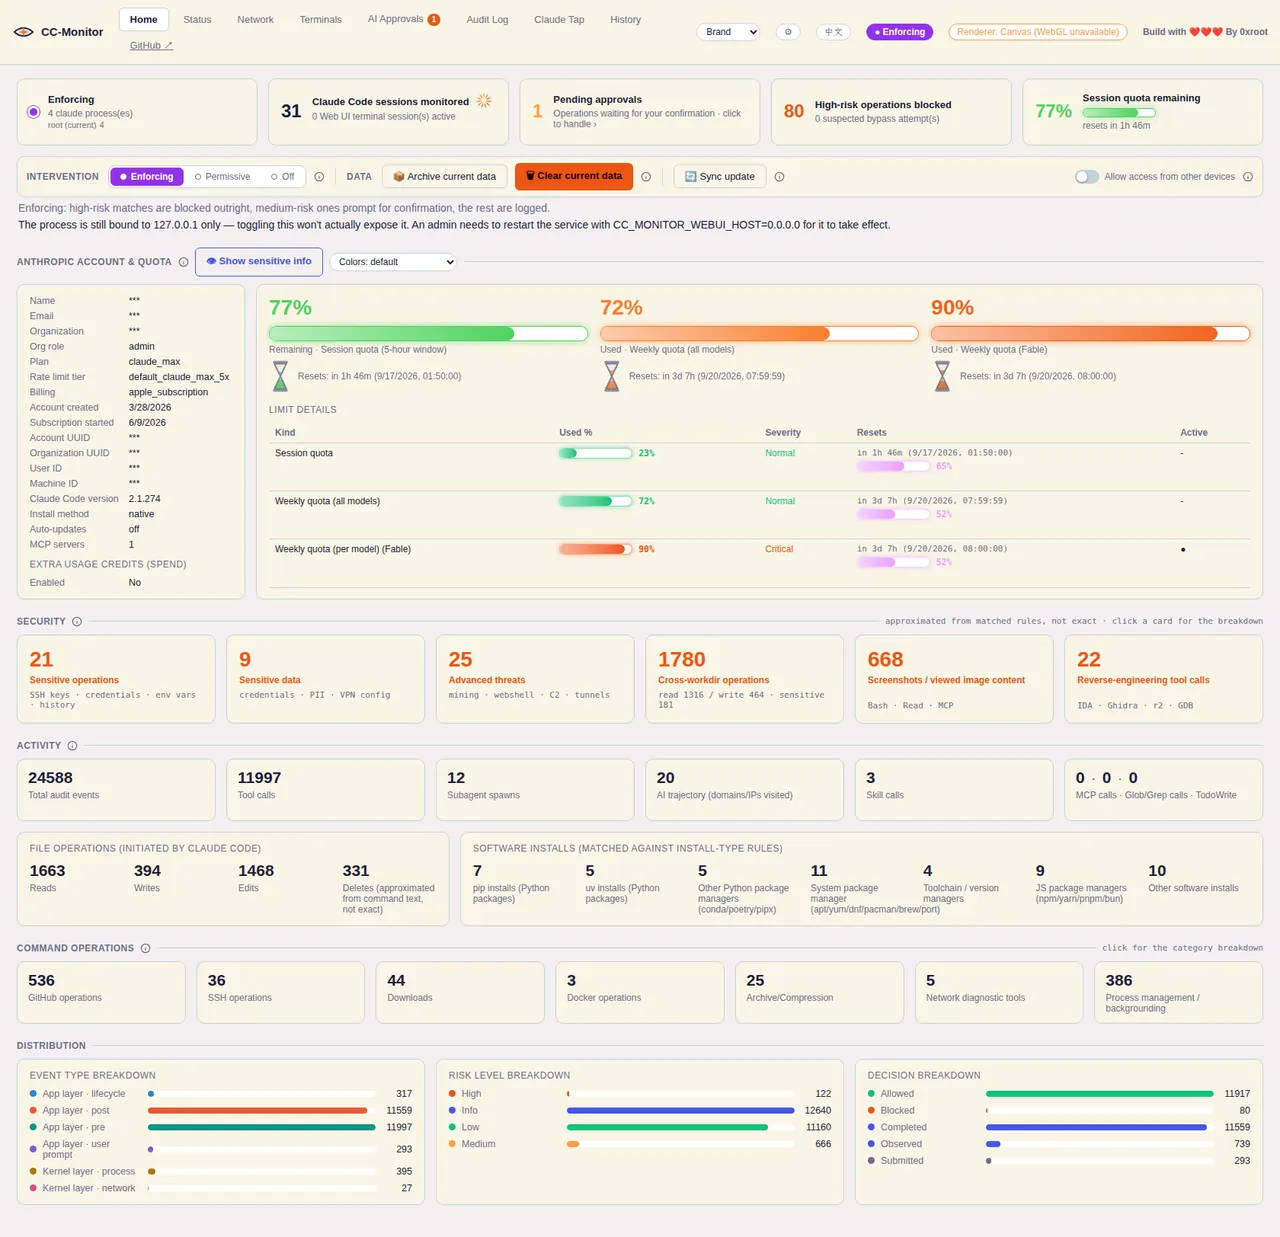
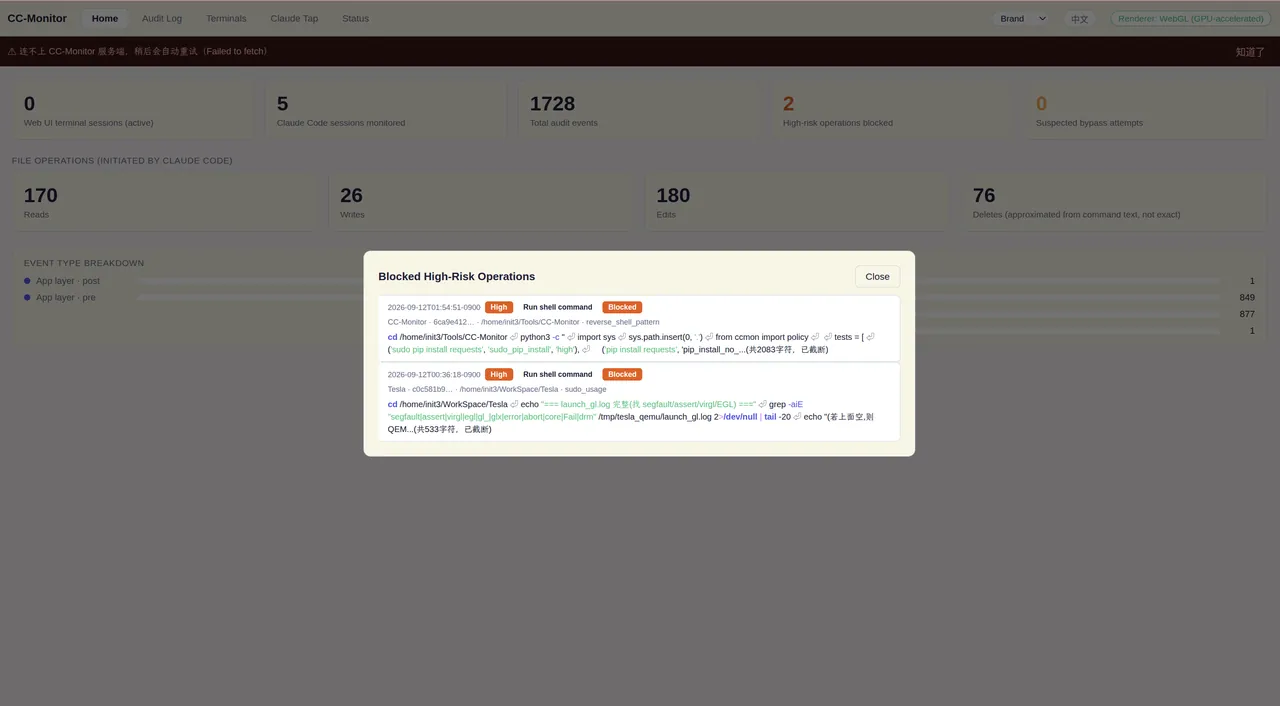
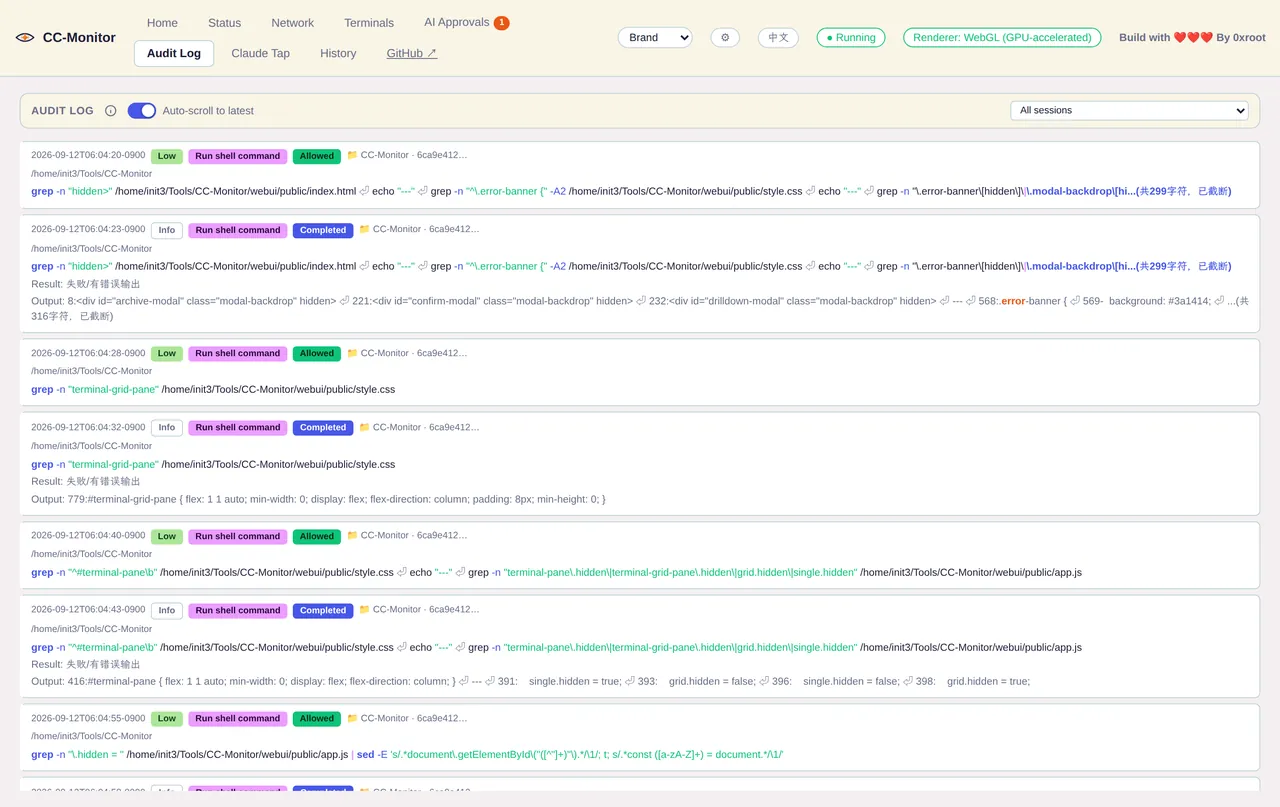
CC-Monitor — Dashboard CC-Monitor — Blocked operations CC-Monitor — Audit log
AI Agent SecurityWebsite

CC-Monitor

cc-monitor.com

See clearly, intercept decisively, audit completely: every action Claude Code takes on your machine

  • Application-layer hooks intercept tool calls before they execute
  • Kernel-level eBPF / nettop verification detects attempts to bypass hooks
  • 87 built-in rules with three response tiers: block, confirm, log
  • 8-page web dashboard, with every audit record stored in SQLite
Zero-dep PythoneBPFSQLiteNode.js
Visit website
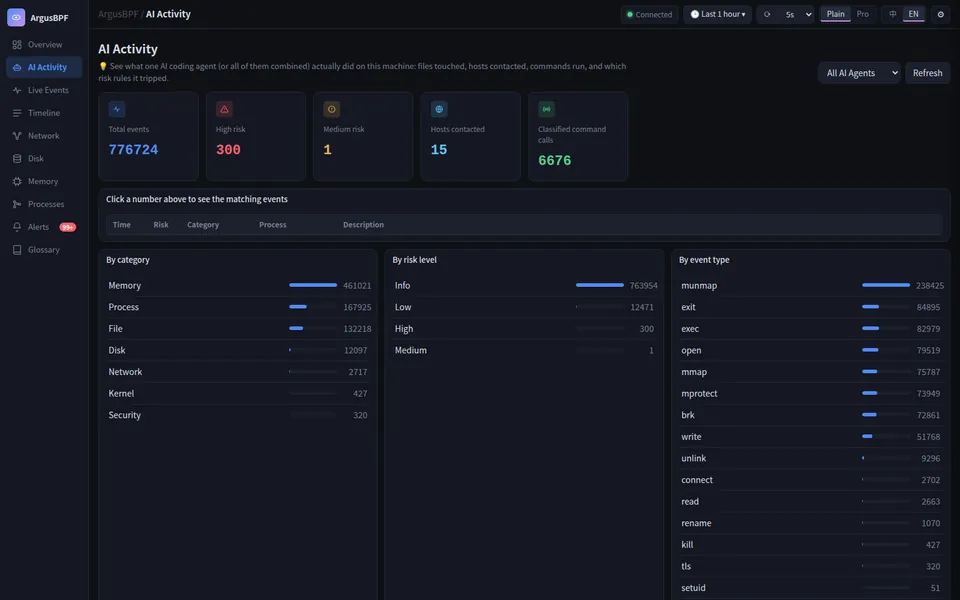
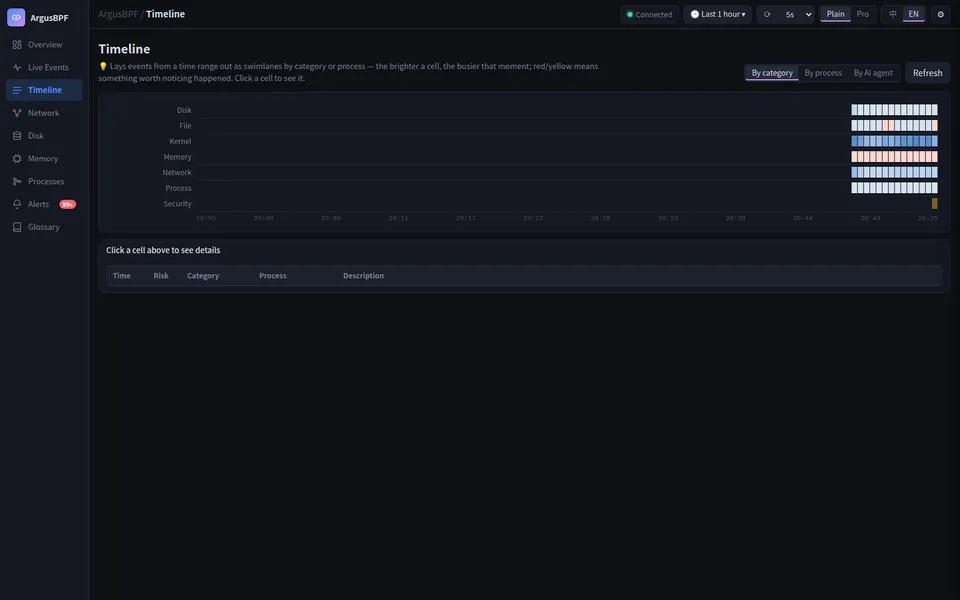
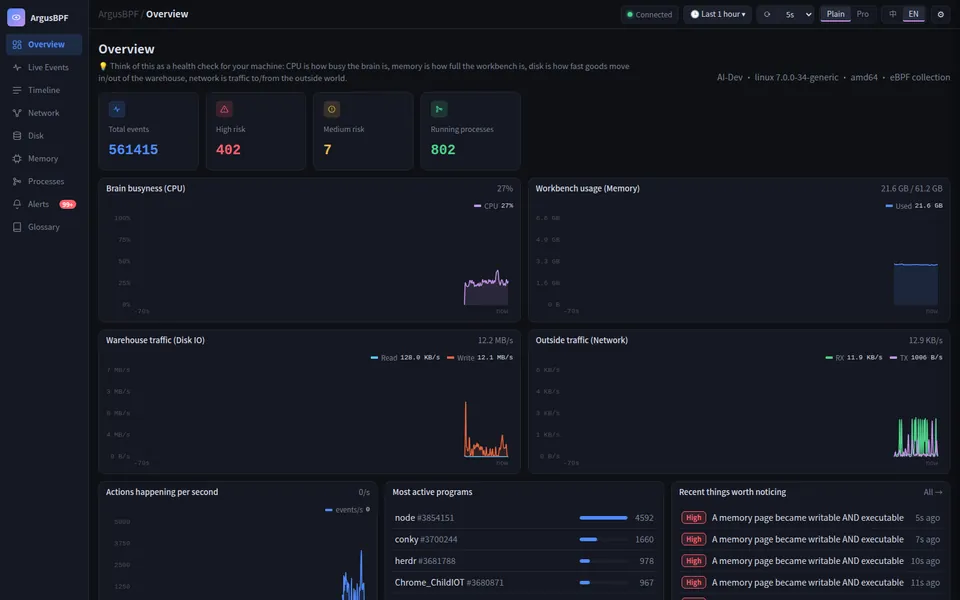
ArgusBPF — Overview ArgusBPF — AI agent activity ArgusBPF — Timeline
AI Agent SecurityOpen source

ArgusBPF

github.com/cn0xroot/ArgusBPF

eBPF-powered visibility into what your OS and AI agents are actually doing

  • Recognizes 10+ AI coding CLIs, including Claude Code, Cursor, and Aider
  • Two views of every event: syscall details plus a contextual explanation
  • uprobes capture plaintext TLS, DNS, and SQL queries
  • Runs as an MCP server so AI assistants can query system activity
GoeBPF CO-REMCPCross-platform
View source
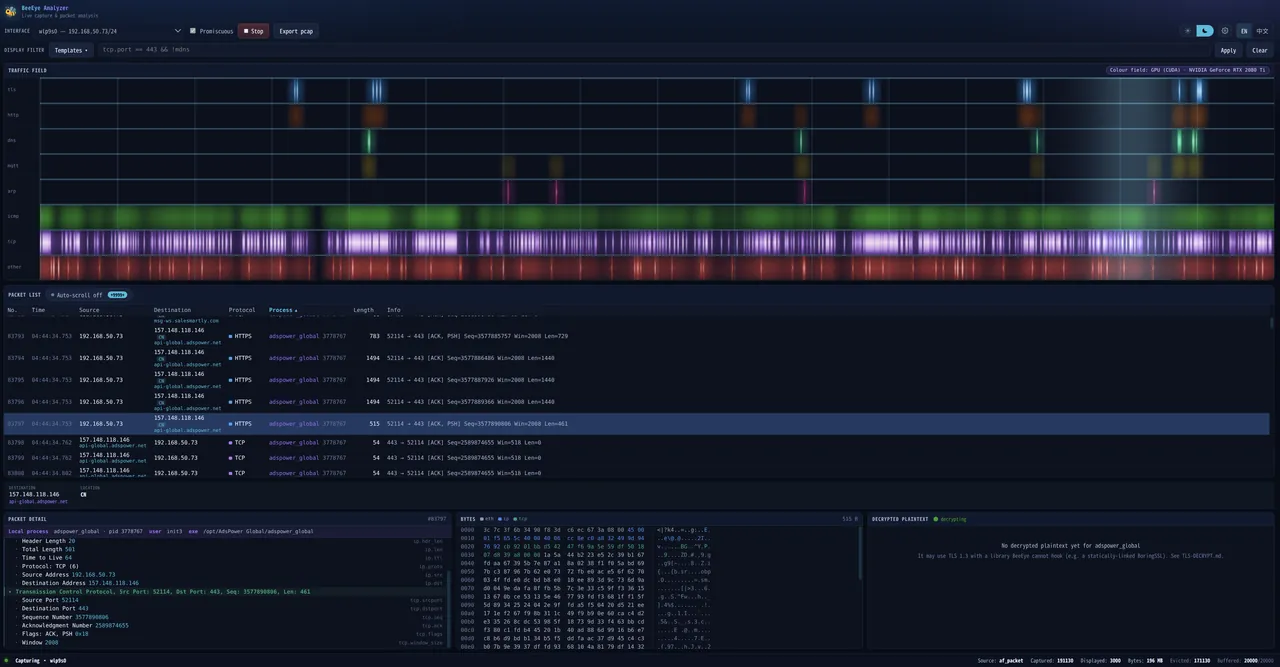
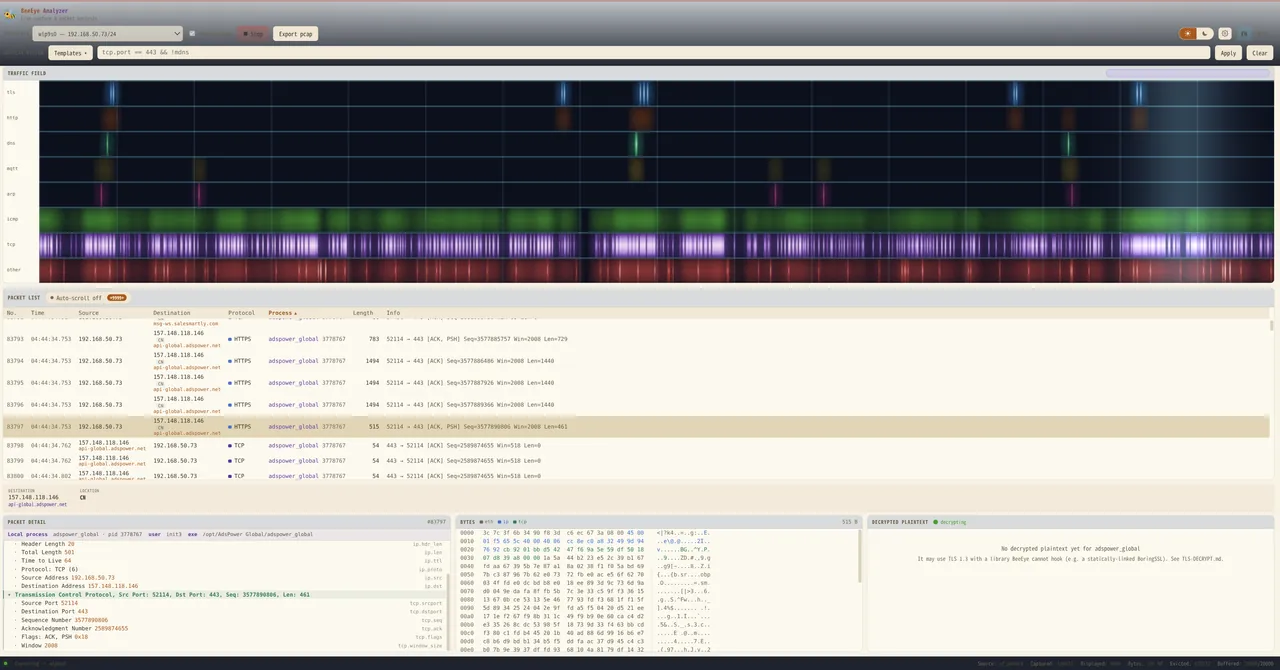
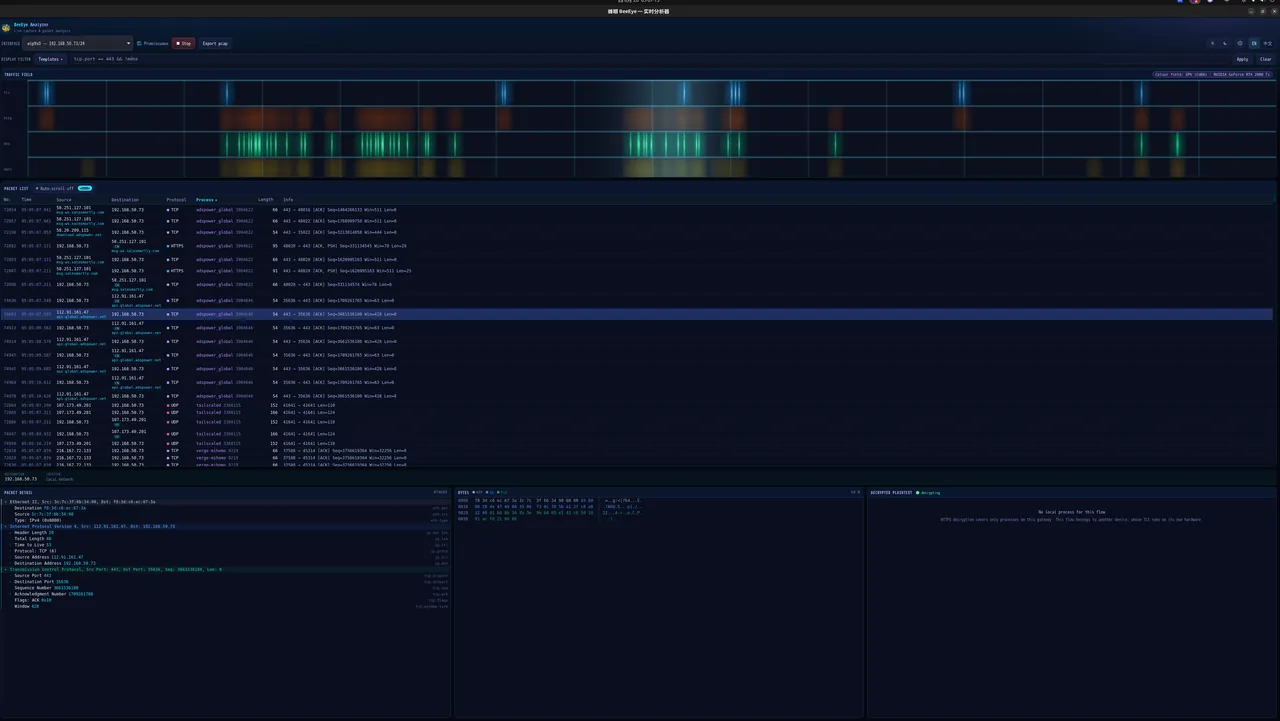
BeeEye — Live analyzer BeeEye — Analyzer · light theme BeeEye — Desktop app
Network & IoT SecurityWebsite

BeeEye

beeeye.dev

Every wingbeat in your hive, visible: eBPF-based home gateway traffic analysis

  • Runs on an Ubuntu gateway, with no agent to install on any device
  • Full protocol dissection from Ethernet to the application layer, with Wireshark-compatible filters
  • 10 weighted detection signals, including beaconing, DNS anomalies, and behavioral baselines
  • Offline GeoIP and no reverse DNS lookups: privacy by design
GoeBPFCUDApcap
Visit website
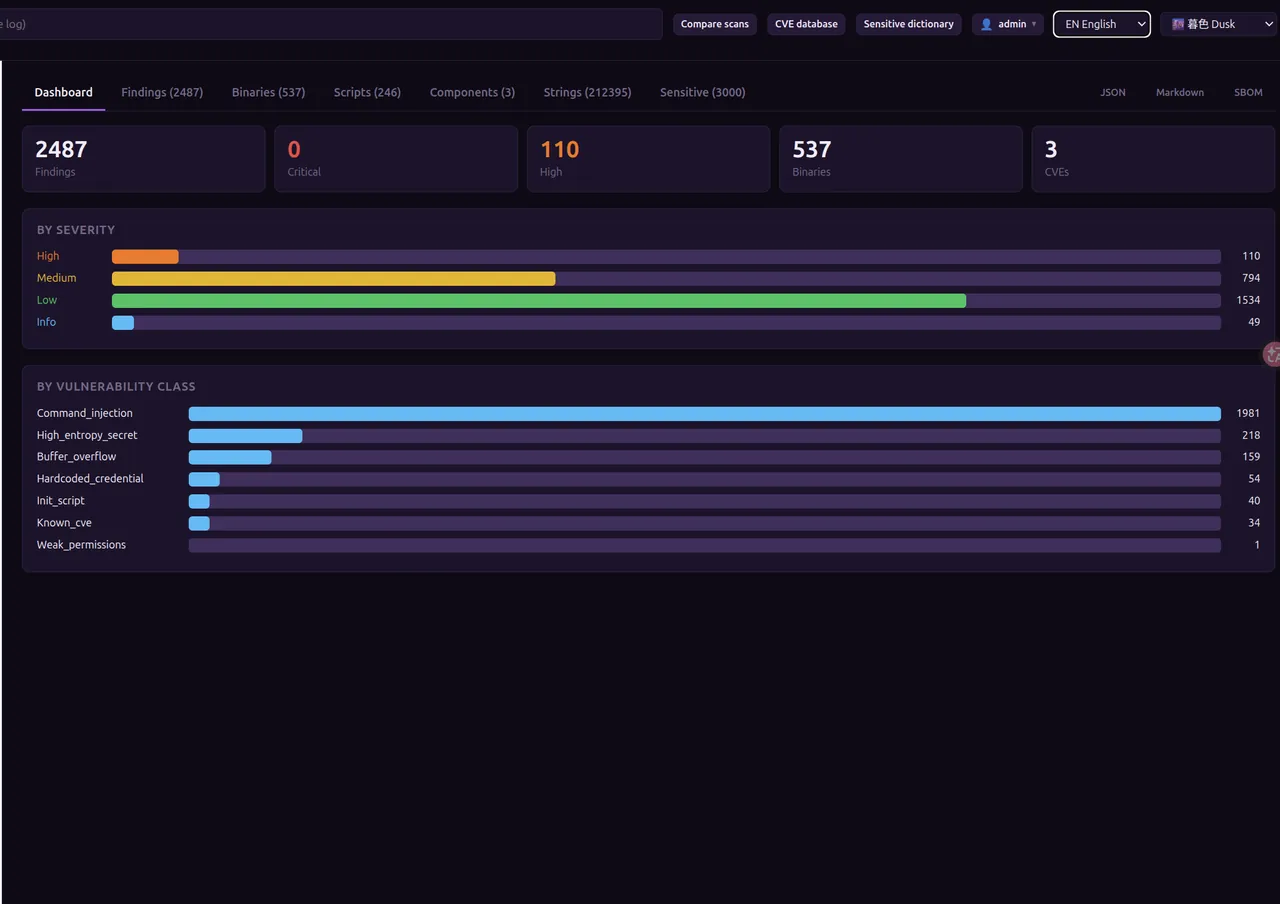
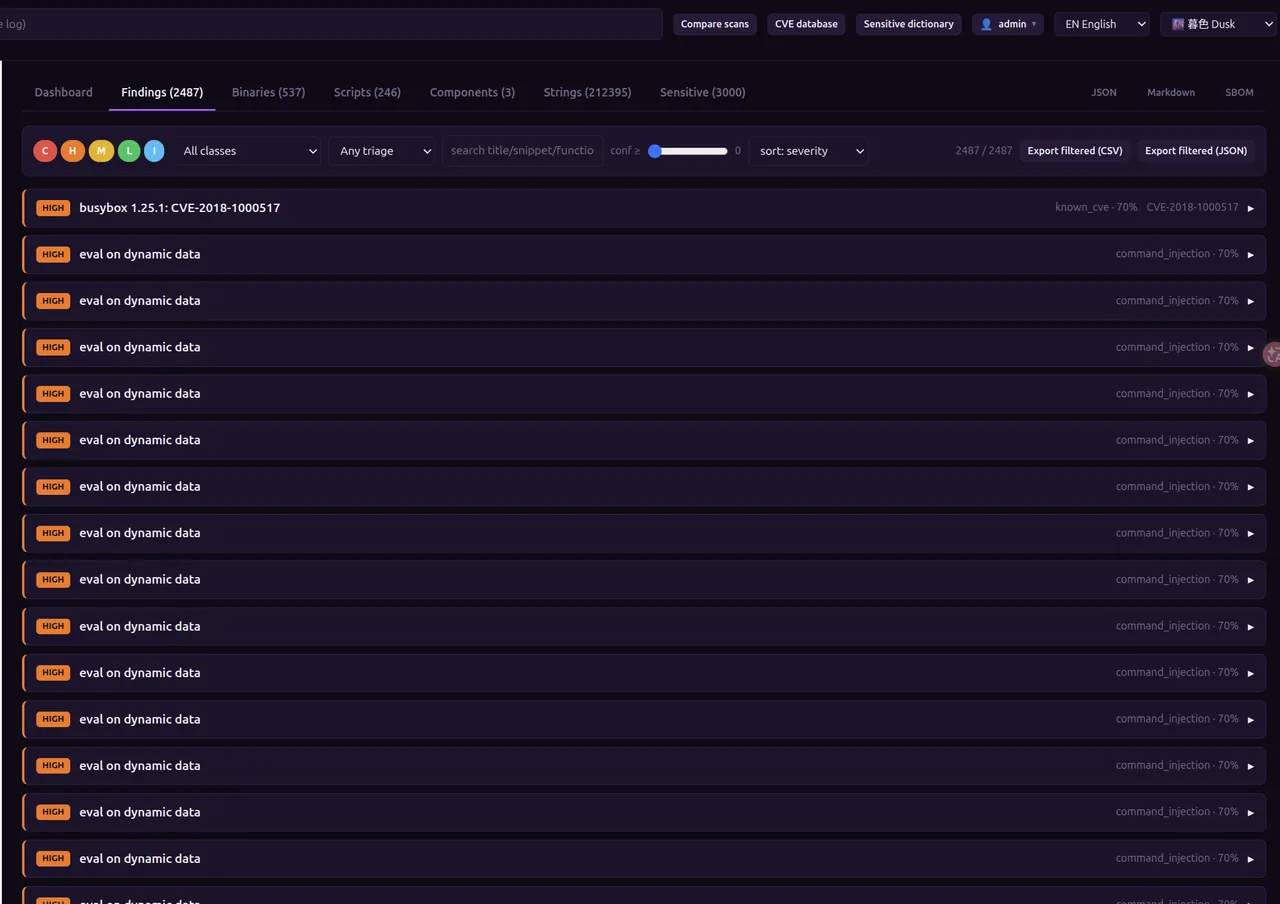
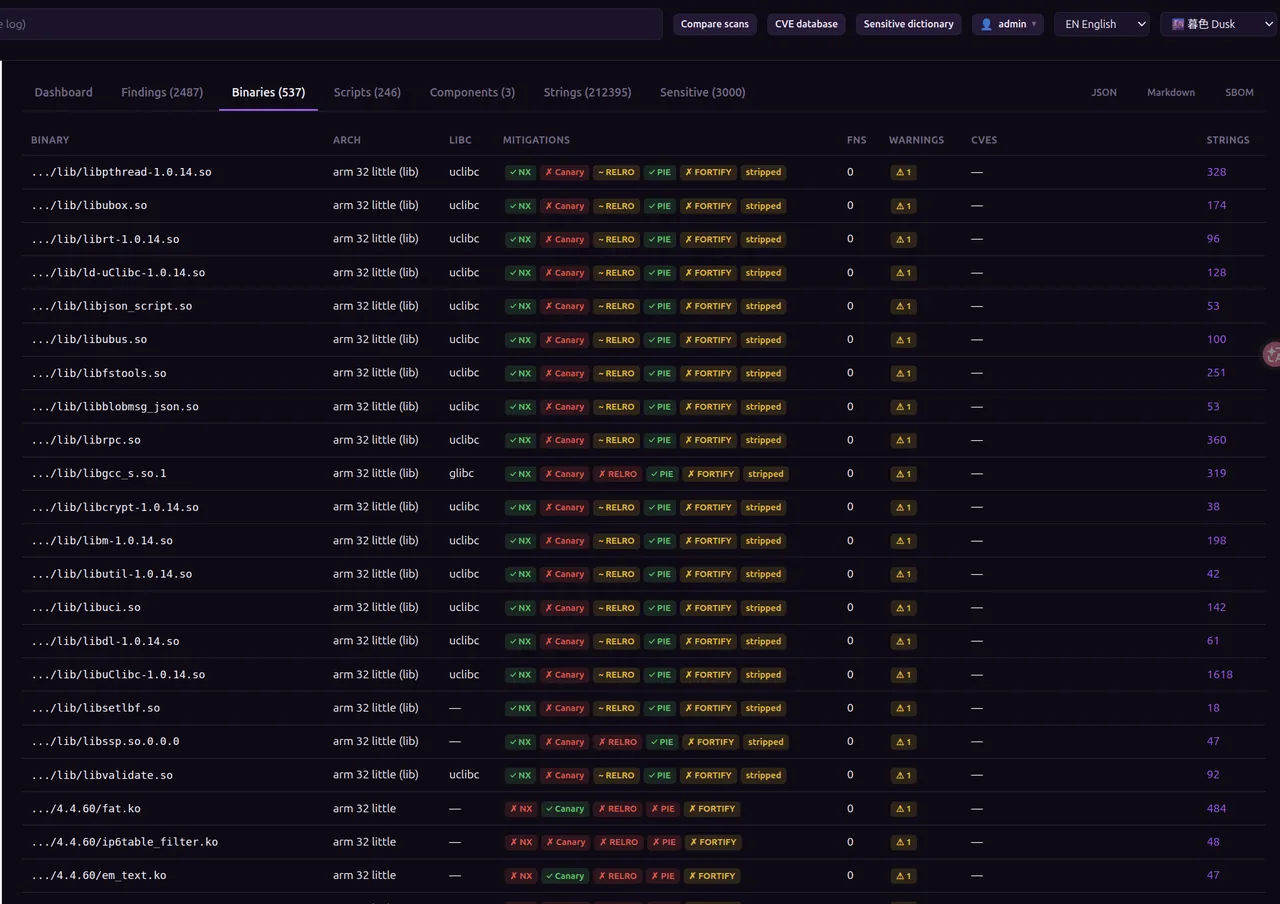
IFDA — Dashboard IFDA — Findings IFDA — Binaries & mitigations
Network & IoT SecurityWebsite

IFDA

ifda.dev

IoT Firmware Deep Analysis: audit every firmware image before it is compromised

  • Multi-architecture disassembly (x86, ARM, MIPS and more), with no physical device required
  • Taint analysis and cross-binary call-chain tracking to uncover attack paths
  • Offline CVE correlation powered by cve-bin-tool
  • AI-assisted triage to filter false positives and prioritize fixes
Reverse engineeringStatic analysisREST APISelf-hosted
Visit website
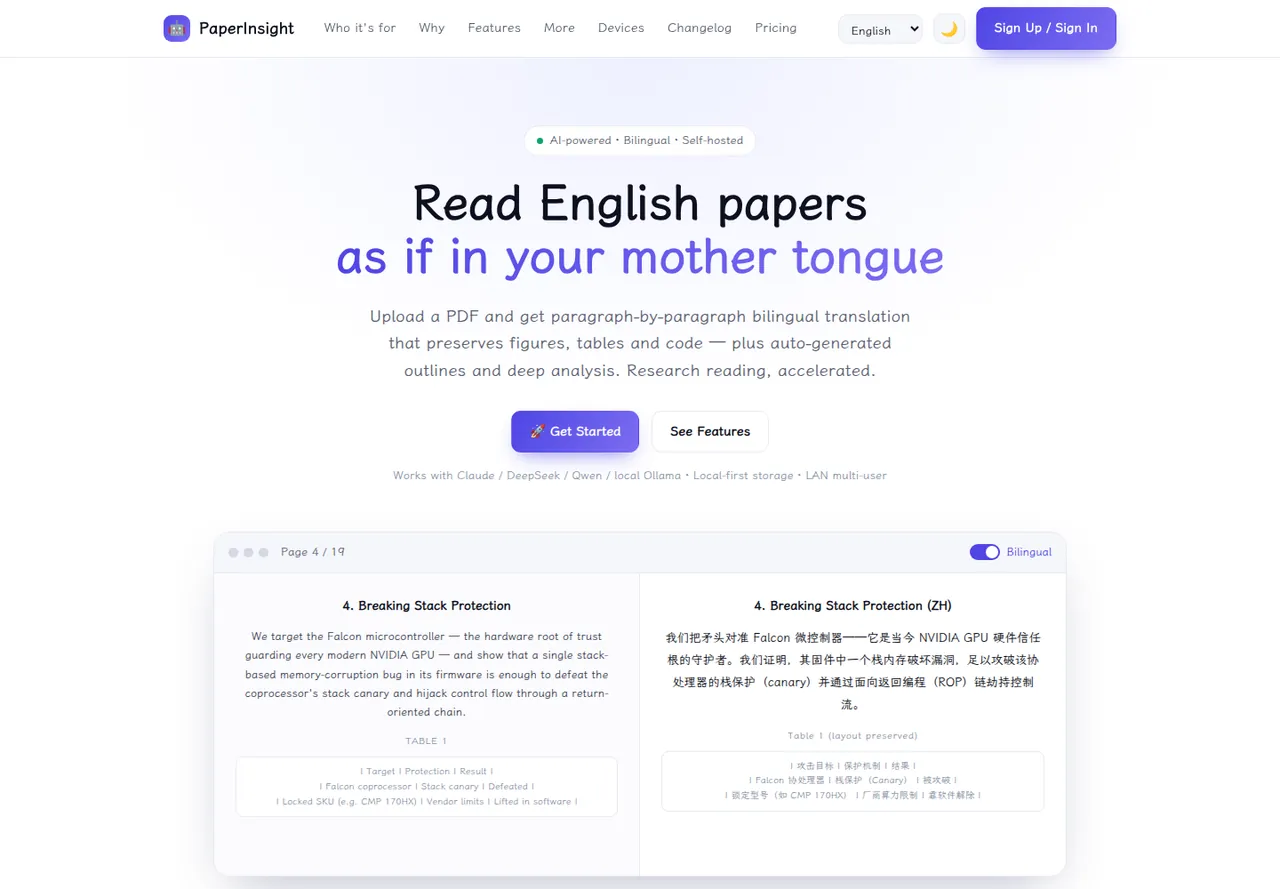
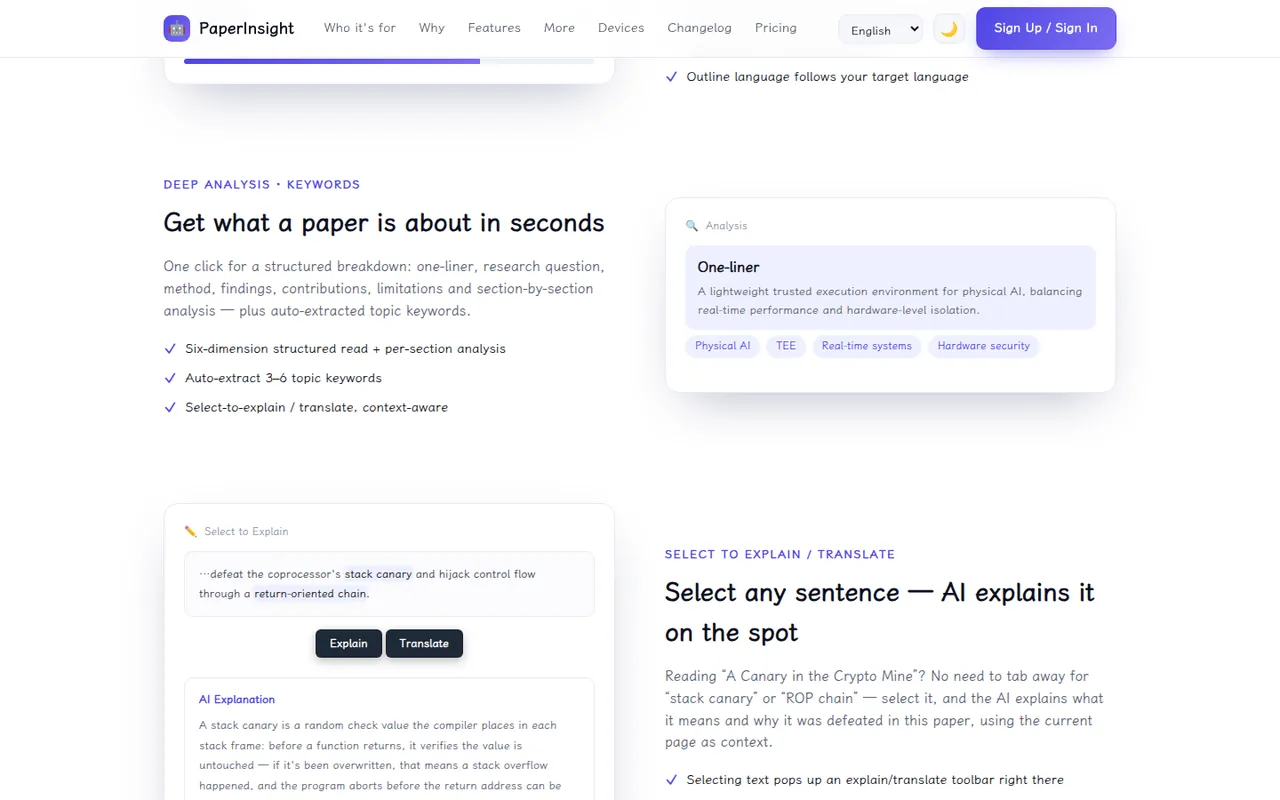
PaperInsight — Bilingual reading PaperInsight — Deep analysis
AI Research ToolsWebsite

PaperInsight

paper-insight.com

Read research papers as easily as text in your native language

  • Original PDF and translation side by side, preserving tables, figures, and code
  • Structured analysis in six dimensions: summary, questions, methods, findings, innovations, limitations
  • Select-to-explain terminology, plus Q&A chat for each paper
  • Works with Claude, DeepSeek, Qwen, and local Ollama models
7 languagesBilingual exportFree tier
Visit website
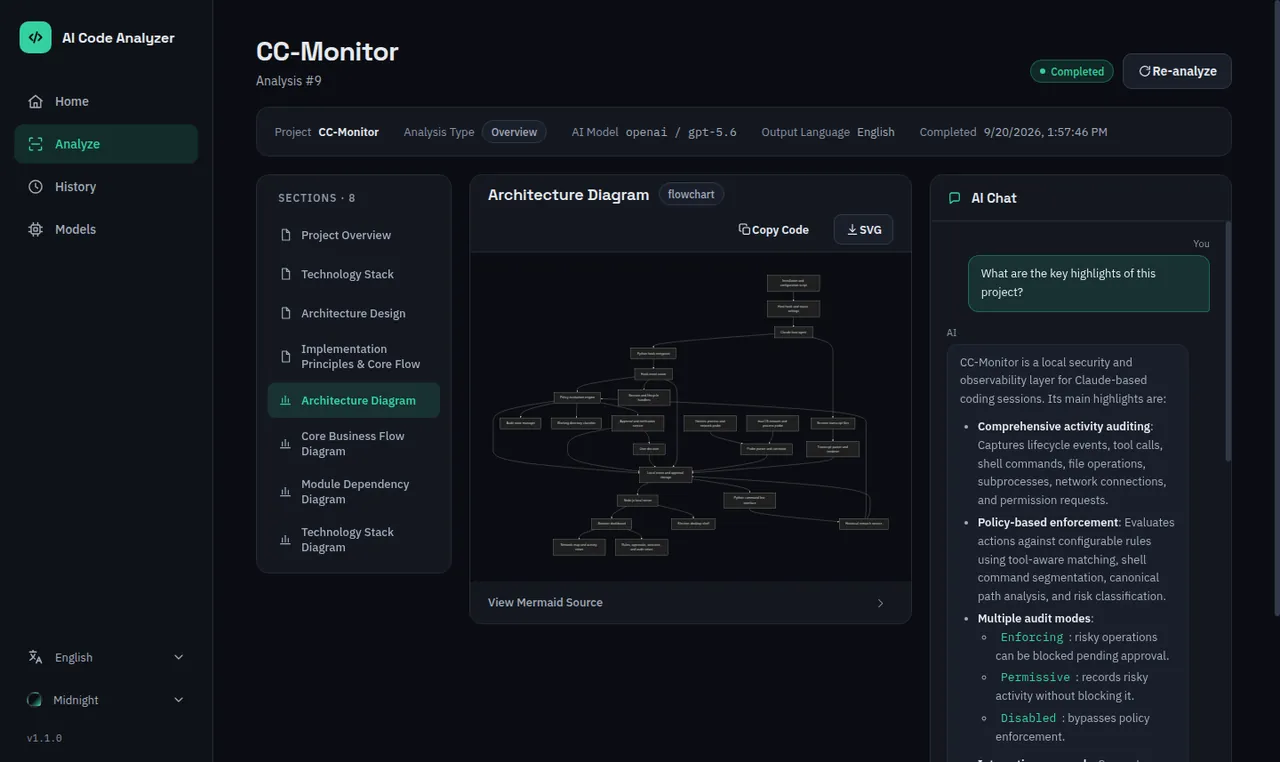
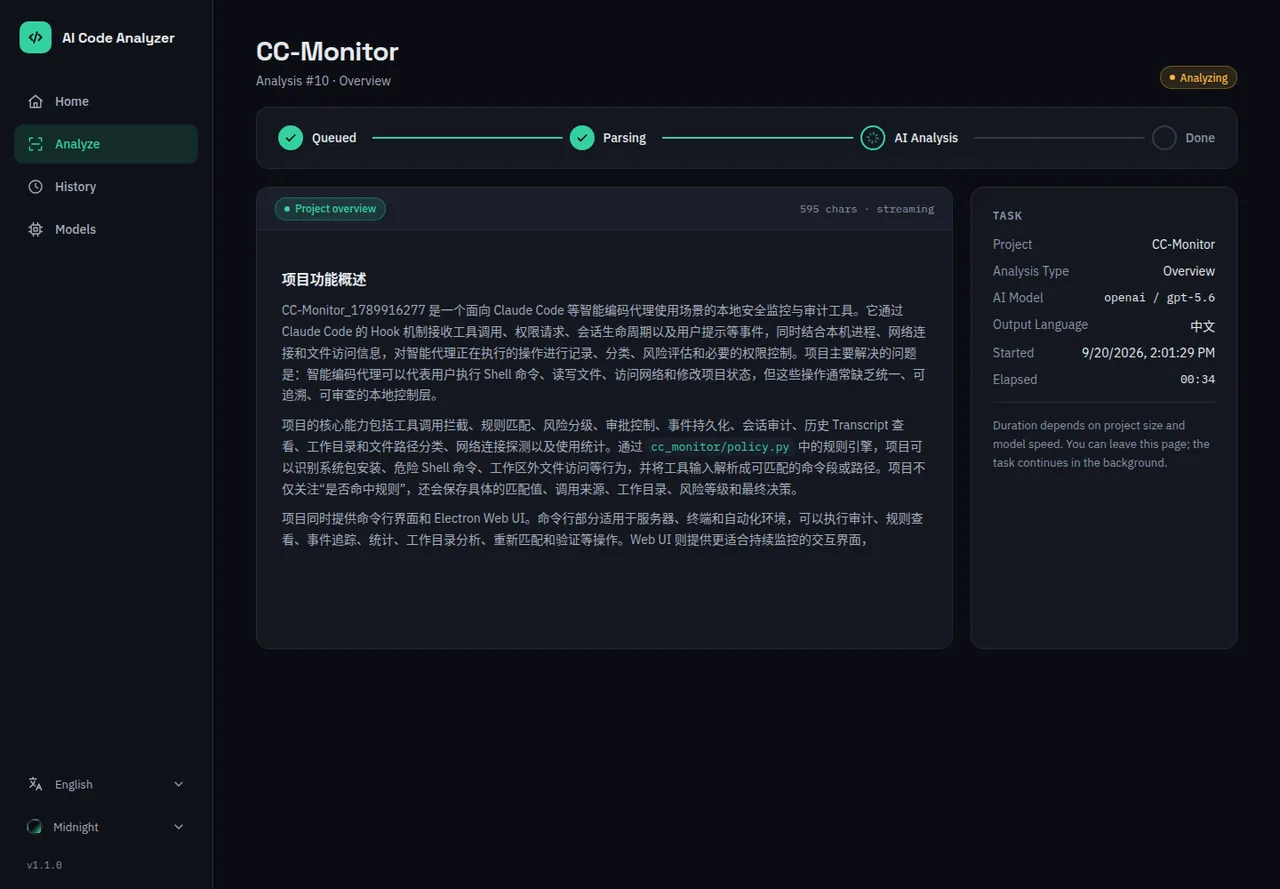
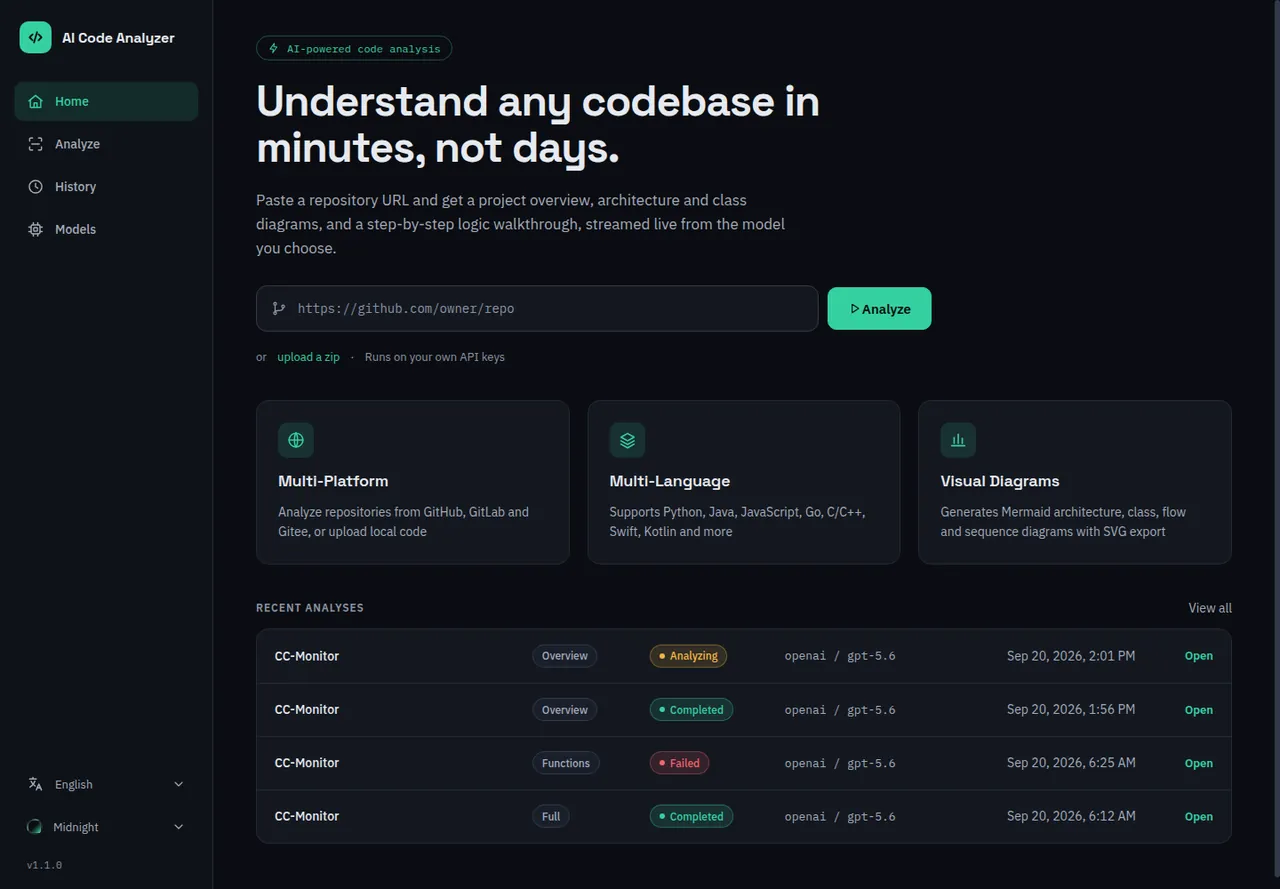
AI Code Analyzer — Analysis result AI Code Analyzer — Streaming analysis AI Code Analyzer — Home
AI Research ToolsOpen source

AI Code Analyzer

github.com/cn0xroot/AI-Code-Analyzer

AI that understands entire repositories and generates architecture docs and diagrams

  • Clone from GitHub, GitLab, or Gitee, or upload local files
  • tree-sitter AST parsing across 305+ languages
  • Generates project overviews, architecture design, and Mermaid diagrams
  • Real-time SSE streaming, with analysis history and re-analysis
FastAPIVue 3tree-sitterMermaid
View source
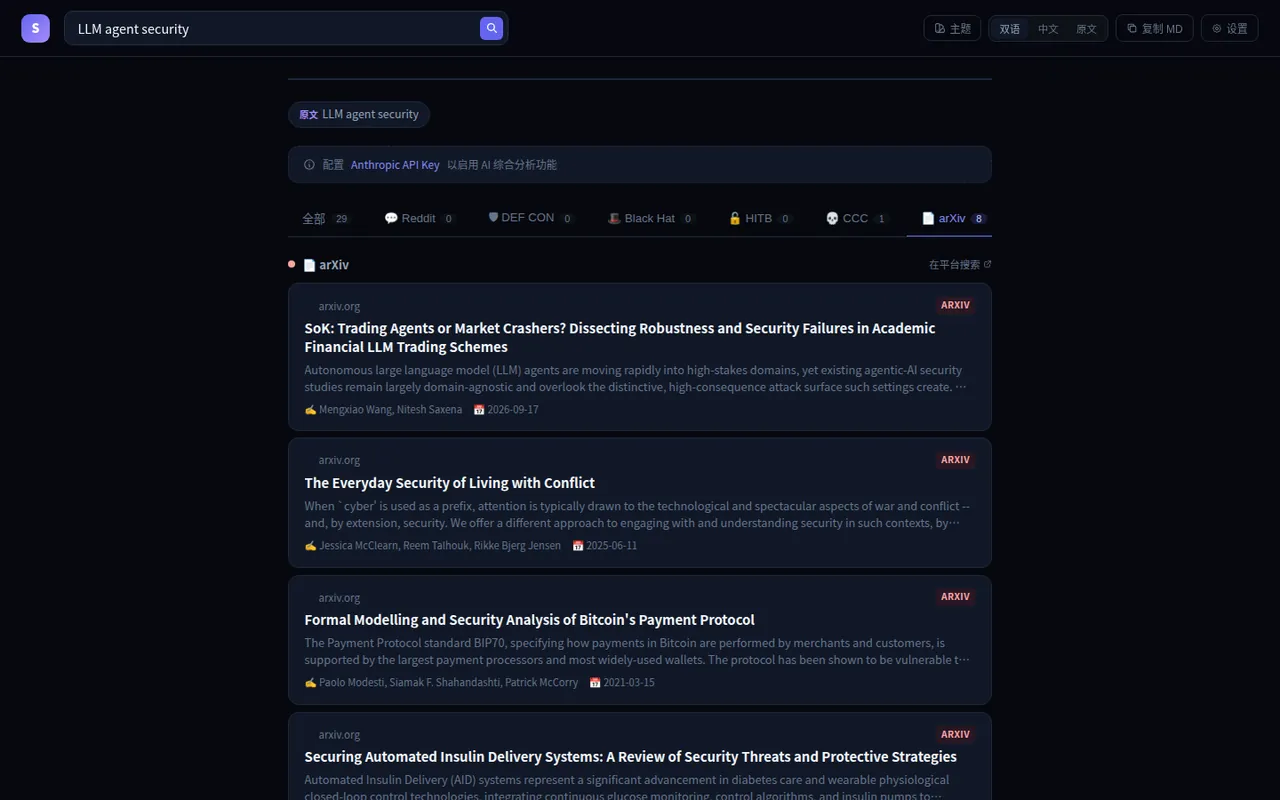
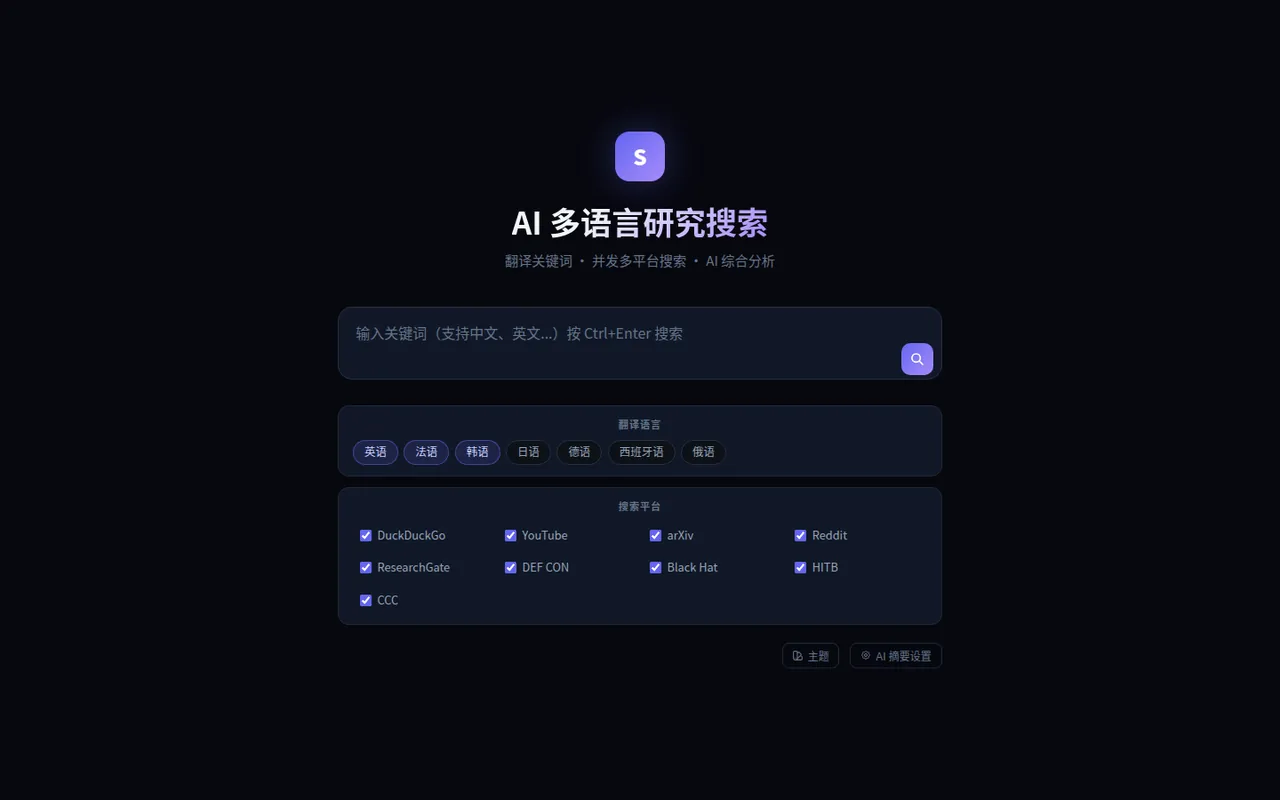
AI Web Search — arXiv results AI Web Search — Search home
AI Research ToolsOpen source

AI Web Search

github.com/cn0xroot/AI_Web_Search

A clean, elegant research search engine with multi-platform aggregation and AI summaries

  • Searches Google, YouTube, arXiv, Reddit, and ResearchGate in parallel
  • Covers security conference archives such as DEF CON, Black Hat, and CCC
  • Translates keywords into multiple languages and re-searches in one click
  • AI-generated summaries with one-click Markdown export
FastAPISSEMultilingual
View source
// PRINCIPLES

How we build

Security tools have to earn trust first. These principles run through every product we make.

01

Local-first

Data lives in local SQLite, and GeoIP and CVE databases work offline, with no third-party cloud dependency.

02

Kernel as ground truth

eBPF observes what actually happens at the kernel level, instead of relying on what applications report about themselves.

03

Explainable behavior

Low-level syscalls and network packets become clear, understandable descriptions of behavior.

04

Open and auditable

Core tools are open source on GitHub. Security tools should be auditable themselves.

L1 · ApplicationHook interceptionDecide before tool calls execute
L2 · Runtimeuprobe probesCapture plaintext TLS, DNS, SQL
L3 · KerneleBPF observationIndependent syscall and network verification
L4 · NetworkGateway analysisNetwork-wide device traffic and anomaly detection
// STACK

Tech stack

Go and eBPF at the core for performance, Python and Vue on top for fast iteration, and swappable LLM backends.

eBPF / CO-REGoPythonFastAPIVue 3tree-sitterSQLiteMCPCUDAClaudeQwenDeepSeekOllamaMermaid
// CONTACT

Building trustworthy AI, together

Try the tools, open an issue, contribute code, or get in touch about collaboration.